Follow @passdb on Twitter
Showing posts with label hacking cyber security. Show all posts
Monday, June 30, 2014
Friday, April 25, 2014
Thursday, April 24, 2014
Grams Darknet Search Engine by Gorvam saddar
All my readers know my involvement in the research conducted on the Tor Network, and in general on the Deep Web.
Recently, many events have shocked the Tor community, the revelation on NSA project to track Tor users, the seizure of the Silk Road black market and the arrest of Eric Eoin Marques, the 28-year-old Irishman owner and operator of Freedom Hosting, the principal hosting service within Tor Network.
Many security experts, me included, have spent their effort to make more accessible the Tor Network, to crawl its content and realize a sort of search engine to rapidly makes search within not indexed pages.
The number of hidden services within the Tor network is impressive, many of them unknown to the majority of the users.
Security experts have discovered that the offer of illicit goods in underground websites is very dynamic, on a daily basis new services offer illegal drugs, weapons, hacking tools, and provide other illegal services to its customers.
Search them within Tor network is often not so easy, users have to know exactly onion URL of the web resource which is difficult to remember.
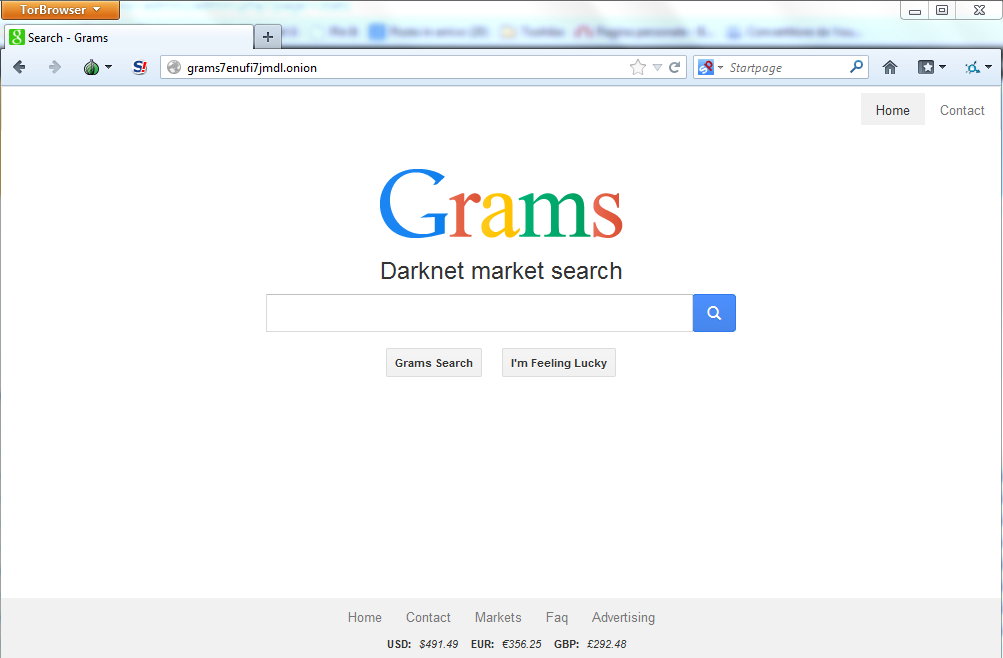
Grams is a project for the implementation of a search engine for online underground Black Markets. It was launched in Beta last week at the address http://grams7enufi7jmdl.onion
Grams can be used by Tor users to easily find sites proposing illegal goods including drugs. Grams’ creator, who uses the nickname of Gramsadmin, announced the release of the beta with a post on Reddit.
Tuesday, April 22, 2014
Optimizing Database For WordPress Websites Automatically [Free Plugin] Gorvam saddar
With time, database of a WordPress website grows in size and can
become quite huge. This is not a problem with WordPress. It is because
your website receives comments, both legitimate and SPAM, and both of
them are stored in database, along with all the posts and pages.
Moreover, all the post revisions that are created whenever you edit a post are also stored in the database. The post revisions may come in handy when you are editing a post, but are of no use once you publish the post. They unnecessarily occupy the database and should be removed from time to time.
You can do all the database Optimization manually, but why not use a free plugin that can run on a schedule and completely on auto-pilot. Optimize Database after Deleting Revisions is a free plugin that can delete post revisions, remove spam comments and delete all the trashed stuff automatically. All the features of this plugin are discussed below.
Moreover, all the post revisions that are created whenever you edit a post are also stored in the database. The post revisions may come in handy when you are editing a post, but are of no use once you publish the post. They unnecessarily occupy the database and should be removed from time to time.
You can do all the database Optimization manually, but why not use a free plugin that can run on a schedule and completely on auto-pilot. Optimize Database after Deleting Revisions is a free plugin that can delete post revisions, remove spam comments and delete all the trashed stuff automatically. All the features of this plugin are discussed below.
Optimize Database After Deleting Revisions
- Deleting Post Revisions: The plugin can delete post revisions that are created whenever you edit a saved/published post. You can set the number of revisions to keep, and the plugin will delete all the revisions beyond them.
Monday, April 21, 2014
Rooting Unix Boxes For Beginners Gorvam saddar
Hello and welcome to rahlabs tutorial on Rooting unix boxes. Today we will learn a few fundementals on what it takes to root a your box! In Today's Tutorial we will be using a linux box.
Required for this tutorial:
Access to a shell - Upload by any-means a shell onto a box
mig-log cleaner
Netcat
Netcat(unix)
Local root Exploit
half a brain
willingness to learn
BackTrack - Basic Usage gorvam saddar
Login to BackTrack
Once the BackTrack is Installed, the default username and password required to log in are root / toor.
NOTE: You will not be able to see the password as you type it.
GUI
- After login give startx command.
- Getting Networking to work
- Setting your IP manually
We will first set up the networking manually. In the following example we will assume the following addresses and their purpose:
IP Address - 192.168.1.112/24
Default Gateway - 192.168.1.1
DNS server - 192.168.1.1.........more
Default Gateway - 192.168.1.1
DNS server - 192.168.1.1.........more
How Web Servers Work BY Gorvam saddar
Let us take a look at the basic working of a web server. What happens when you type http://gorvam.blogspot.in/
in your browser?
.htaccess Tutorial by Gorvam Saddar
- Part 1 - Introduction
- Part 2 - .htaccess Commands
- Part 3 - Password Protection
Introduction
In this tutorial you will find out about the .htaccess file and the power it has to improve your website. Although .htaccess is only a file, it can change settings on the servers and allow you to do many different things, the most popular being able to have your own custom 404 error pages. .htaccess isn't difficult to use and is really just made up of a few simple instructions in a text file.
How to patch your server against The Heartbleed Bug
What is the Heartbleed Bug?
The Heartbleed Bug is a serious vulnerability in the popular OpenSSL cryptographic software library. This weakness allows stealing the information protected, under normal conditions, by the SSL/TLS encryption used to secure the Internet. SSL/TLS provides communication security and privacy over the Internet for applications such as web, email, instant messaging (IM) and some virtual private networks (VPNs).
Shell by LFI - Method proc / self / environ by Gorvam saddar
Shell by LFI - Method proc / self / environ
1 - Introduction
2 - Discovery LFI
3 - check if / proc / self / environ is accessible
4 - malicious code injection
5 - Access to the shell
6 - Thanks
In this tutorial I will show how to obtain a shell on a site using your Local File Inclusion and
injecting malicious code in proc / self / environ.Este a tutorial that explains everything step by step.
- Now a site to find a vulnerable target to Local File Inclusion.Am found to verify
www.website.com/view.php?page=contact.php
2 - Discovery LFI
3 - check if / proc / self / environ is accessible
4 - malicious code injection
5 - Access to the shell
6 - Thanks
>> 1 - Introduction
In this tutorial I will show how to obtain a shell on a site using your Local File Inclusion and
injecting malicious code in proc / self / environ.Este a tutorial that explains everything step by step.
>> 2 - Discovery LFI
- Now a site to find a vulnerable target to Local File Inclusion.Am found to verify
www.website.com/view.php?page=contact.php
VoIP Hacks: How to Spoof Your Caller ID by Gorvam saddar
A fun prank is to call friends, family, or strangers from the White House's phone number (202 456-2121). The reason that this is possible is that Vonage, Skype, and other VoIP providers fundamentally must be able to fake caller ID in order to route calls from the internet onto public phone networks (so presumably they've been doing some lobbying over the years).
A Brief Technical Overview of Caller ID Spoofing:
What we'll do is register a free account at an ITSP, or Internet Telephony Service Provider, which acts as the bridge between the internet and the public American (or otherwise) analog telephony networks. We'll then configure the ITSP to use the White House's phone number as our outbound caller ID. Finally, we'll connect to the ITSP using a free VoIP client, or softphone, to make our call using a PC.
The 10-Minute Step-by-Step Process:
Joomla SQL Injection ....!!! by Gorvam saddar
Joomla SQL Injection
hacked Joomla websites
is that a SQL injection vulnerability was exploited. A typical URL which
is affected by this type of vulnerability looks like this:index.php?option=com_blabla&category=5&Item=2
Typically the following parameters are vulnerable:
Hacking Web Servers by Gorvam saddar
The popular web servers are Apache Web Server, Internet Information Server and Sun ONE Web Server.
The Apache Web Server is an open-source web server for modern operating systems including UNIX and Windows NT. The server provides HTTP services in sync with the current HTTP standards in an efficient and extensible environment.
The Java Web Server / Sun ONE Web Server is one of the other highly available Web servers on the market. Microsoft's Internet Information Server is another popular server used by a sizable percentage of websites.
Threat | Common Security Risks |
XSS cheat sheet by Gorvam saddar
XSS cheat sheet
Before we start what is XSS? let's come to basic !! hmm what is cookie , don't say something like eating stuff.
COOKIE:
A cookie is the variable that
web-browsers use to store your login credentials. Without a cookie, you
cannot "stay logged in" on websites.
CROSS SITE SCRIPTING:
Cross-Site Scripting is the process of injecting JavaScript (mainly) and also HTML into a webpage.
SOME POINTS ON XSS :
@ -XSS attacks almost always focus upon sites which use cookies for storing our username and password.tRAdiTIOnAL Type$: type0 , type1, type2
@-XSS is used to harm the website (may be defacing ).
Install Backtrack 5 On Samsung Galaxy Tab by Gorvam saddar
Install Backtrack 5 On Samsung Galaxy Tab
First thing after I get Samsung Galaxy Tab 10.1 is how can I change or add some feature about penetration testing to my Tab. So after I read "How to install Backtrack5 on Motorola Xoom by Pual[.]com, I think I can install Backtrack 5 in my Tab too. That's it. I create this tutorial after I'm successful to installing Backtrack 5 on my Tab. But please do all the steps with you risk!!!!.
1. Download rooting file and transfer it to the tab.
2. Go into the recovery mode with hold "Power Button and Low Volumn Button" for rebooting and when you see the 2 icon press "Low Volumn" and press "High Volumn" or "Power Button" for go to recovery mode.
3. Choose "apply the update from sdcard" and choose "rooting file"
After this step, you're tab was rooted now.
Tutorial on How to Hack Terminal Services by Gorvam saddar
Tutorial on How to Hack Terminal Services
TSGrinder is readily available from http://www.hammerofgod.com/download.html.
TSCrack you'll have to google for as it is not readily available anymore.
Rdesktop v1.41 can be downloaded from http://www.rdesktop.org/ and you'll need the patch from foofus.net http://www.foofus.net/jmk/rdesktop.html.
Part 1: MS Terminal Services Overview
Hacking Exposed Windows Server 2003 goes a great overview, I won't plagiarize it all here, so check it out for me details and the references section of this paper for some MS references.Prior to Terminal Services, Windows did not provide the ability to run code remotely in the processor space of the server. Another way to put this is there was no way to have an "interactive" session on the server. There were tools like wsremote or psexec or VNC. If an attacker got a non administrator level account on a remote machine they could map shares and copy files but had a difficult time running code on the server. Now, with Terminal Services, an attacker can log on as a non privileged user and run exploit local exploit code via the Terminal Services GUI. These attacks used to be fairly limited to local physical attacks or from users who actually logging into your domain but now if the server has Terminal Services (2000 server 2003 server) or RDP (Windows XP) running the attack vector increases.
SMS Spoofing with Kali Linux by Gorvam Saddar
SMS Spoofing with Kali Linux
Social Engineering toolkit
How to detect a hacker attack by gorvam saddar
How to detect a hacker attack
Most computer vulnerabilities can be exploited in a variety of ways. Hacker attacks may use a single specific exploit, several exploits at the same time, a misconfiguration in one of the system components or even a backdoor from an earlier attack. Due to this, detecting hacker attacks is not an easy task, especially for an inexperienced user. This article gives a few basic guidelines to help you figure out either if your machine is under attack or if the security of your system has been compromised. Keep in mind just like with viruses, there is no 100% guarantee you will detect a hacker attack this way. However, there's a good chance that if your system has been hacked, it will display one or more of the following behaviours.
Sunday, April 20, 2014
Snort by gorvam saddar
Introduction to Snort
1
Introduction to Snort
A lightweight Intrusion Detection System by Marty Roesch
Document based extensively on original snort documentation from /usr/local/share/snort
1
Introduction to Snort
A lightweight Intrusion Detection System by Marty Roesch
Document based extensively on original snort documentation from /usr/local/share/snort
Introduction to Snort
2
Using Snort
What is snort?
Snort is a lightweight intrusion detection system that can log packets coming across your network. This
Subscribe to:
Posts (Atom)
_Cartoonized.jpg)